As your practice grows, so does the complexity of keeping your technology running smoothly, your patient data secure, and your operations compliant. Healthcare IT consulting planning for growing practices is not just a technical exercise — it is a strategic priority that affects your staff productivity, your regulatory standing, and your ability to serve patients without disruption. Whether you are adding providers, opening a second location, or simply trying to keep up with evolving compliance requirements, having a structured IT plan in place is essential.
Why Growth Exposes IT Gaps You Did Not Know You Had
Many medical practices operate for years on IT systems that were set up once and rarely revisited. That approach works until it doesn’t. Growth — whether in staff size, patient volume, or service lines — tends to reveal weaknesses that were always there but manageable at a smaller scale.
Common signs that your IT setup has not kept pace with your practice include:
- Staff losing time daily to slow systems, login errors, or disconnected software
- Your EHR, phones, and network are not communicating effectively, causing workarounds and manual steps
- New providers or locations were added without updating access controls, user accounts, or security policies
- Vendors and software tools have multiplied without a clear review process
- No one is sure who manages what when a technology problem occurs
These are not just inconveniences. Each gap represents a potential compliance exposure, a patient safety risk, or a source of costly downtime.
Building a Technology Plan That Actually Works for Your Practice
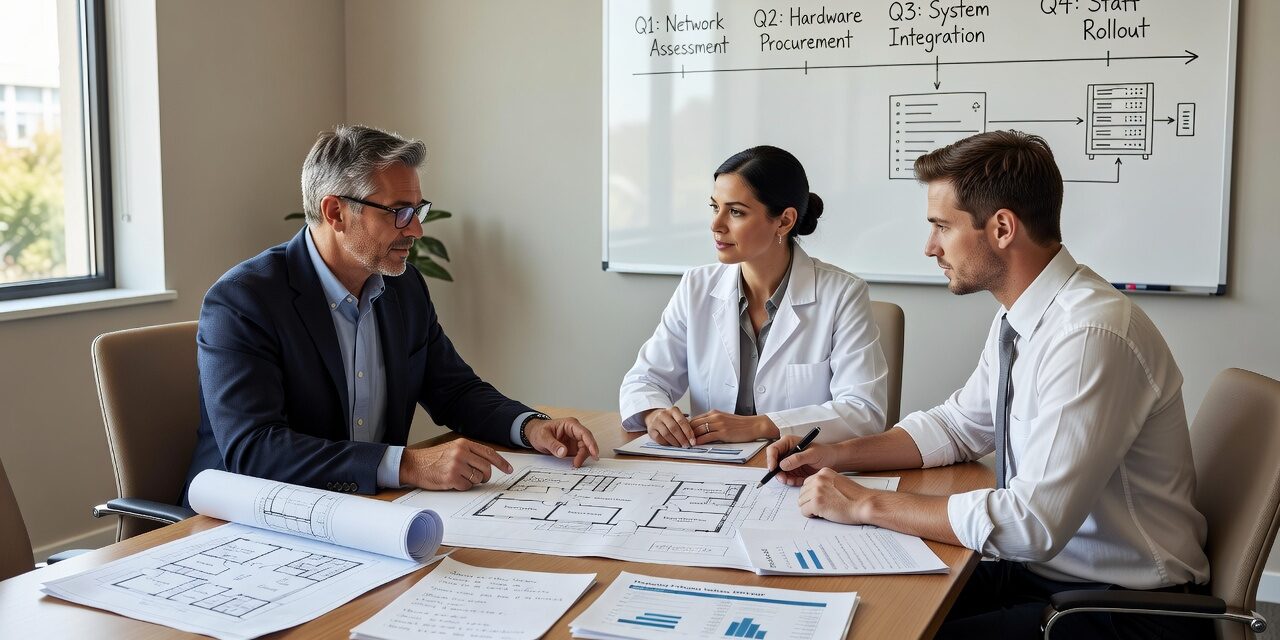
A practical technology plan does not require a massive budget or a full IT department. What it does require is structured thinking about where your practice is now, where it is headed, and what technology decisions need to be made proactively rather than reactively.
Start With an Honest Inventory
Before making any changes, document what you currently have:
- All software platforms in use, including EHR, billing, scheduling, and patient communication tools
- Hardware age and condition across all workstations and devices
- Current vendors and what each one is responsible for
- Who has access to what systems, and whether those access levels are still appropriate
- When your last security review or compliance assessment was completed
This inventory often surfaces quick wins — outdated user accounts that should have been removed, software subscriptions that are redundant, or systems that are end-of-life and no longer receiving security updates.
Prioritize by Risk, Not by Cost
Not every IT project needs to happen at once, but some carry significantly more risk than others. A good planning framework helps you sequence decisions based on what protects the practice most, not just what seems most urgent in the moment.
High-priority items typically include:
- Security and access controls: Reviewing passwords, multi-factor authentication, and user permissions across all systems
- Backup and recovery: Confirming that patient data is backed up reliably and can be restored quickly if something goes wrong
- Vendor accountability: Knowing which third-party vendors have access to your systems or patient data, and whether Business Associate Agreements are in place
- End-of-life hardware and software: Replacing systems that no longer receive security patches, which are a common entry point for ransomware
For multi-location practices, access controls and network segmentation deserve especially close attention, since a vulnerability at one location can affect the entire organization.
Common IT Planning Mistakes Medical Practices Make During Growth
Even well-run practices fall into predictable traps when they grow quickly or manage IT reactively. Recognizing these patterns early can save significant time and expense.
Relying on break-fix IT support beyond its useful stage. Break-fix support — calling someone when something breaks — works for very small practices with simple setups. Once you have multiple providers, locations, or complex EHR integrations, you need proactive monitoring and planning, not just reactive fixes. The cost of unplanned downtime in a busy clinic almost always exceeds the cost of a structured support arrangement.
Adding new software without a formal review process. Every new application added to your environment introduces potential compatibility issues, security considerations, and compliance questions. Before adding any new tool, evaluate how it handles patient data, whether it requires a Business Associate Agreement, and how it integrates with existing systems.
Skipping annual technology planning reviews. Technology does not stay static, and neither do compliance requirements. A yearly review of your IT environment — covering security, access, vendors, and hardware — helps your practice stay ahead of problems rather than scrambling to fix them.
Not documenting your cybersecurity policies. Regulators expect medical practices to have written policies covering how patient data is protected, who has access, how incidents are reported, and how the practice would recover from a disruption. Undocumented policies are treated the same as no policies during an audit.
How to Prepare for a Compliance Readiness Review
If you have not recently reviewed your security posture, preparing for a compliance review is one of the most valuable planning exercises your practice can do. It does not need to wait for an audit notice. In fact, the practices that fare best during regulatory reviews are those that treat compliance as an ongoing operational discipline rather than a once-a-year scramble.
A basic compliance readiness checklist for medical practices should include:
- Review all user accounts and access levels — remove former employees, update roles for staff changes
- Confirm backup systems are working — a backup that has never been tested is not a reliable backup
- Audit third-party vendor agreements — confirm BAAs are signed and up to date for all vendors handling PHI
- Document your incident response plan — what happens if a breach or ransomware attack occurs?
- Review your security risk documentation — regulators look for evidence of ongoing risk evaluation, not just a one-time assessment
For practices that have never completed a formal review, healthcare risk assessment guidance can help identify where to start and what documentation is expected.
Questions to Ask When Evaluating IT Support for a Growing Practice
If your practice is considering a move from informal or reactive IT support to a more structured arrangement, asking the right questions upfront will help you find a provider who understands healthcare’s unique requirements.
Key questions to ask any IT support candidate:
- Do you have experience working specifically with medical practices and healthcare compliance requirements?
- How do you handle HIPAA compliance documentation and support?
- What does proactive monitoring look like, and how quickly do you respond to issues?
- Can you support multiple locations under a single, coordinated plan?
- How do you handle vendor management and third-party software integrations?
- What happens to our data if we end our relationship with you?
A provider with genuine healthcare IT experience will answer these questions clearly and without hesitation. For practices evaluating IT support planning for growing clinics, it also helps to ask for references from practices of similar size and complexity.
What This Means for Your Practice
Growing medical practices face a predictable set of IT challenges: systems that were never designed to scale, compliance requirements that grow more complex each year, and staff who lose time daily to technology friction that should not exist. The good news is that most of these challenges are addressable with planning, not just spending.
A structured approach to healthcare IT consulting and planning — one that prioritizes security, documents what you have, and sequences decisions by risk — can significantly reduce your exposure to compliance penalties, ransomware, and operational disruption. You do not need to solve every problem at once. You need to know what your problems are, which ones matter most, and have a clear plan to address them.
If your practice has grown in the past two years and your IT plan has not kept pace, now is the right time to take stock. Start with an inventory, identify your highest-risk gaps, and build from there. The practices that manage IT proactively protect their patients, their staff, and their financial stability far more effectively than those who wait for something to go wrong.
—
Ready to take the next step? Contact the MedicalITG team for a straightforward conversation about where your practice stands and what a practical IT plan would look like for your specific situation.